GravityRAT
- 194
- Global rank
- 158
- Month rank
- 128
- Week rank
GravityRAT is a sophisticated spyware and remote access trojan that has been actively targeting organizations and government entities since 2016. It uses innovative anti-analysis techniques and made an evolution from a Windows-only threat to a cross-platform espionage tool capable of compromising Windows, Android, and macOS systems.
- RAT
- Type
- Unknown
- Origin
- 1 January, 2016
- First seen
- 14 October, 2026
- Last seen
How to analyze GravityRAT with ANY.RUN
IOCs
IP addresses
- 31.58.77.222
- 23.59.18.102
- 48.192.1.64
- 135.233.95.144
- 40.126.31.130
- 23.11.40.157
- 48.209.138.189
- 204.79.197.203
- 95.100.135.122
- 172.211.123.250
- 2.16.204.135
- 2.16.204.155
- 150.171.109.106
- 135.233.95.135
Hashes
- 71453523c85ae94798b4935f8519f4bac0f7c53c0c99f4f5e24c3a8a1e5fab22
- 5f4afc766685e909e0c6803d916a2605f8b0db1975d0a442fcb0a1682ad52e12
- 43b222d2d25fe79b9839385823f4140651bc66e194fe06df912baafcd0ade768
Domains
- ocsp.digicert.com
- oneocsp.microsoft.com
- fe3cr.delivery.mp.microsoft.com
- www.microsoft.com
- ecs.office.com
- settings-win.data.microsoft.com
- crl.microsoft.com
- slscr.update.microsoft.com
- client.wns.windows.com
- th.bing.com
- google.com
- self.events.data.microsoft.com
- login.live.com
- www.bing.com
- cdnlabng.mylogisoft.com
- activation-v2.sls.microsoft.com
URLs
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
- http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- https://login.live.com/rst2.srf
- https://login.live.com/ppsecure/deviceaddcredential.srf
- https://th.bing.com/th?id=odswg.iotdlocalicon&w=16&h=16&c=1&rs=1&p=0
- http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
- https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
- https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
- https://slscr.update.microsoft.com/sls/ping
- https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
- https://th.bing.com/th?id=ohr.ammonitefossils_en-us6354038755_1920x1080.jpg&w=392&h=221&c=1&rs=1&p=0
- https://th.bing.com/th?id=ocge.gameasset_9nhcntdg1blm_e88e0edb-8e3c-4482-add0-115dcfc7cd60&w=86&h=86&c=1&rs=1&p=0
- https://th.bing.com/th?id=obtq.bt2f991fae281dce5c97daef7d04528db39d8161fcf6da96ee0474cc969aa7b202&w=190&h=154&c=1&rs=1&p=0
- https://th.bing.com/th?id=ocge.9mz3sdptqwm2_v4_main&w=86&h=86&c=1&rs=1&p=0
- https://th.bing.com/th?id=ocge.9nm5764dbppg_abtesting_e1200f50-f281-4ee6-9d31-7b45fb226e4a&w=86&h=86&c=1&rs=1&p=0
- https://th.bing.com/th?id=ocge.9npxcz4n8jw7_v3_main&w=86&h=86&c=1&rs=1&p=0
- https://th.bing.com/th?id=ocge.gameasset_9n7hl5s06zk0_f62e3da5-2500-443c-9a62-58a0a4c8cb87&w=86&h=86&c=1&rs=1&p=0
Last seen at
GravityRAT: Comprehensive Defense Against the Malware That Outsmarted Sandboxes for a Decade
Key Takeaways
- GravityRAT is a multi-platform RAT focused on espionage, with strong ties to targeted campaigns against Indian entities.
- It excels at data exfiltration, including sensitive files and WhatsApp backups on Android devices.
- It often arrives via spear-phishing, malicious macros in documents, or trojanized apps masquerading as legitimate software.
- Patient social engineering through social media has proven here more effective than mass phishing campaigns.
- Its anti-VM checks make automated sandbox evasion a real challenge. Detection and prevention require updated EDR, behavioral monitoring, and strict app/email policies.
- TI Lookup accelerates IOC correlation to quickly identify GravityRAT indicators across infrastructure. Search by the RAT’s name to explore sandbox analysis sessions and gather indicators.
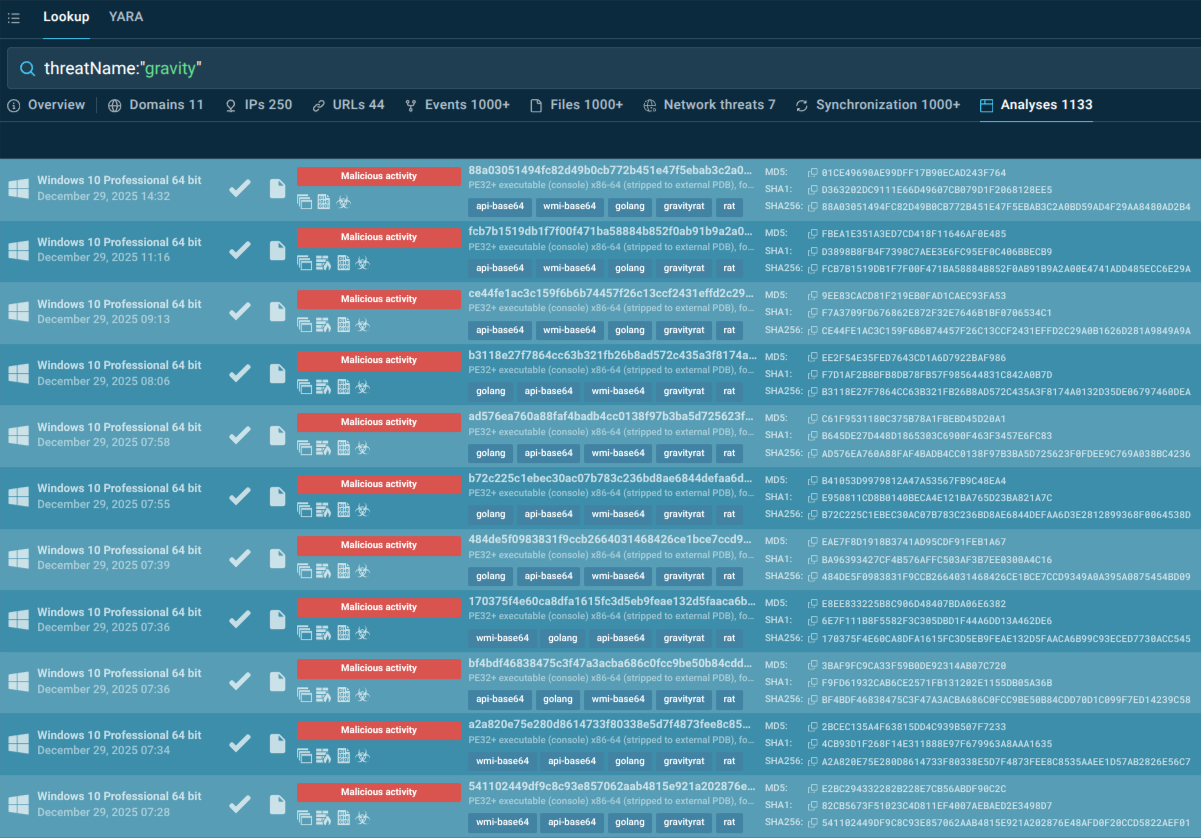
- ANY.RUN’s Sandbox is capable of uncovering malicious behaviors that evade static detection and lets analyze moble as well as desktop-endpoint malware.
What is GravityRAT Malware?
GravityRAT is a remote access trojan designed for long-term espionage operations. The malware has undergone continuous development over nearly a decade, with operators consistently adding new capabilities while maintaining the same command-and-control infrastructure.
The threat demonstrates remarkable persistence and sophistication, utilizing digital signatures to appear legitimate, employing multiple programming languages (.NET, Python, Electron), and disguising itself as various legitimate applications including secure messaging apps, file-sharing tools, media players, and cloud storage services.
The malware's most distinctive feature is its extensive use of anti-virtual machine and anti-sandbox techniques. Researchers have identified seven different VM detection methods employed by GravityRAT, including checking BIOS versions, searching for hypervisor artifacts, counting CPU cores, and most notably, querying CPU temperature through Windows Management Instrumentation.
This temperature check is particularly effective because most hypervisors including Hyper-V, VMware Fusion, VirtualBox, KVM, and Xen do not support temperature monitoring, causing them to return error messages that immediately reveal the presence of a virtual environment.
The malware operates through a sophisticated infrastructure managed by GravityAdmin, a custom administration panel that allows operators to coordinate multiple campaigns simultaneously. Each campaign operates under specific codenames such as FOXTROT, CLOUDINFINITY, CHATICO for Android-based infections, and CRAFTWITHME, SEXYBER, and CVSCOUT for Windows-based attacks using the HeavyLift loader.
GravityRAT Malware Victimology
GravityRAT campaigns have predominantly targeted entities within the Indian subcontinent, with a particular focus on military organizations, government agencies, defense contractors, police departments, and other sensitive institutions. The threat actor behind GravityRAT, attributed to Pakistani state-sponsored groups with tactical overlaps to Transparent Tribe (also known as APT36), has expanded its targeting beyond military and government sectors to include educational institutions and commercial enterprises.
Between 2016 and 2018, approximately 100 infections were documented among defense, police, and government employees in India. More recent campaigns from 2022 through 2024 have shown continued activity, including the attempts to compromise WhatsApp backups and target both Indian military personnel and individuals within the Pakistan Air Force. The highly targeted nature of these campaigns is evidenced by distribution methods that require specific credentials, geographic locations, or time windows to access malicious download sites.
How GravityRAT Malware Gets in and Functions
GravityRAT typically spreads through targeted spear-phishing emails containing malicious Office documents with macros or exploits for Windows infections. On Android, it disguises itself as legitimate apps, such as fake messaging platforms (e.g., BingeChat, Chatico, or SoSafe Chat), distributed via third-party sites or social engineering. It does not self-propagate laterally but relies on initial access through social engineering, with recent campaigns combining Android trojans and Windows loaders like HeavyLift.
When macros are enabled, the malicious code copies the document to a temporary directory, renames it as a ZIP archive, decompresses it to extract the executable payload, and creates a scheduled task to execute the malware while maintaining persistence.
The RAT operates through a multi-stage infection and command-and-control architecture. Upon initial execution, the malware first performs extensive environment checks to determine if it's running in a physical machine or a virtual/sandbox environment. These checks include querying the MSAcpi_ThermalZoneTemperature WMI entry for CPU temperature, examining BIOS versions for VM indicators (VMware, Xen, AMI), searching for VM hypervisor artifacts, analyzing MAC addresses for known VM prefixes, and counting CPU cores.
If the malware determines it's running on a real system, it proceeds to establish persistence through scheduled tasks and begins its data collection operations. The malware communicates with its command-and-control infrastructure via HTTP, typically using PHP endpoints with variant-specific URI paths. For example, different versions contact paths like /ROMEO/[hash].php or /TANGO/[hash].php. Initial connections often retrieve dynamic C2 addresses from hardcoded domains, allowing operators to rotate infrastructure while maintaining control.
GravityRAT implements a modular architecture where different components handle specific functions. The Android version, for instance, uses background services that periodically contact C2 servers, sending IMEI identifiers and device status while awaiting commands. The malware employs AES encryption for certain operations, with some versions using distinctive strings like "lolomycin2017" as encryption salts. File exfiltration occurs in batches, with the malware creating ZIP archives of collected documents before transmission to attacker-controlled servers.
The GravityAdmin panel provides operators with real-time visibility into infected systems, displaying lists of compromised machines organized by campaign codename and offering buttons to trigger various malicious actions against one or multiple systems simultaneously. This centralized management enables efficient coordination of large-scale espionage operations across multiple campaigns.
Sandbox Analysis of a GravityRAT Sample
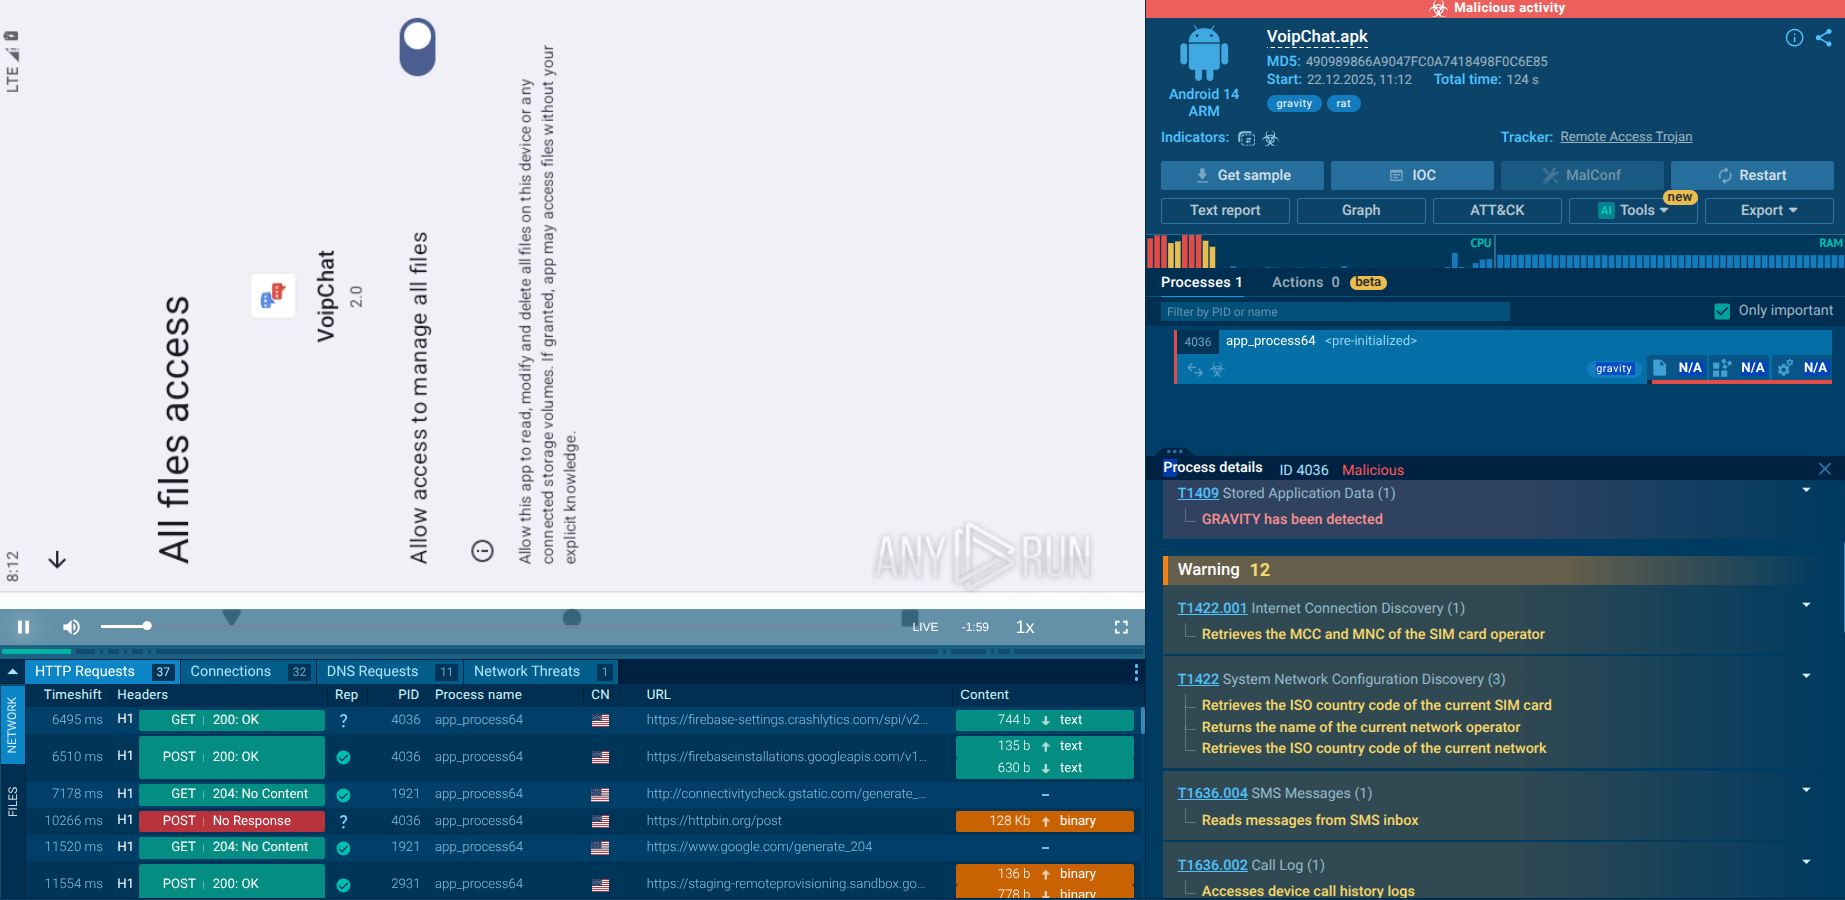
ANY.RUN’s Interactive Sandbox provides isolated, instrumented environments where security researchers and analysts can safely execute suspicious files without risking production systems.
View a GravityRAT sample analysis
The analyzed sample is disguised as a messaging app and is typically distributed through websites that advertise a “free messenger.”
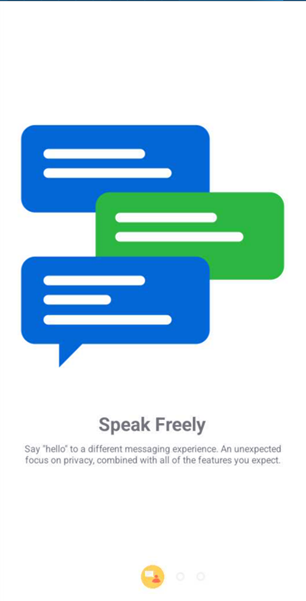
App appearance
The malicious APK presents itself as “Speak Freely,” an allegedly encrypted messaging app with the tagline:
“Say ‘Hello’ in a different messaging experience. An encrypted focus on privacy, combined with all of the features you expect.”
Network information collection
GravityRAT retrieves the MCC and MNC of the SIM card operator, the SIM card’s country ISO code, the name of the current network operator, and the current network’s ISO code. This allows the malware to verify the device’s network configuration and confirm internet connectivity, which is required for further communication with the C2 server.
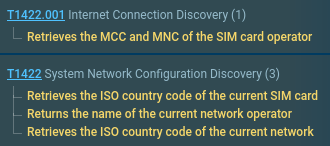
Observed MITRE ATT&CK techniques (network discovery):
- T1422.001 Retrieves the MCC and MNC of the SIM card operator,
- T1422 System Network Configuration Discovery.
File and directory scanning
The malware scans files and directories, listing file names without full paths to identify potential exfiltration targets (T1420 File and Directory Discovery – Get file name without full path).
Data theft
GravityRAT extracts SMS messages and call logs from protected user data, saving them in text files (e.g., /storage/emulated/0/bc/ms.log) before exfiltrating them to the C&C server.
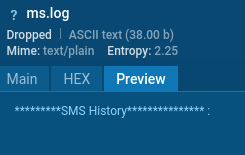
Observed MITRE ATT&CK techniques:
- T1636.004 SMS Messages – Reads messages from SMS inbox,
- T1636.002 Call Log – Accesses device call history logs.
The malware also targets files with extensions such as .jpg, .pdf, .txt, and WhatsApp backups.
Exfiltration and cleanup
Stolen files are sent to the attacker and then deleted from the device (in the case of logs). Communication with the C2 server uses HTTPS, providing an encrypted channel for data exfiltration and command reception.
Observed MITRE ATT&CK technique: T1521 Encrypted Channel – Establishing a connection.
It is worth emphasizing once again the importance of installing applications only from trusted sources and not from random websites—this practice significantly reduces the risk of device infection.
Gathering Threat Intelligence on GravityRAT Malware
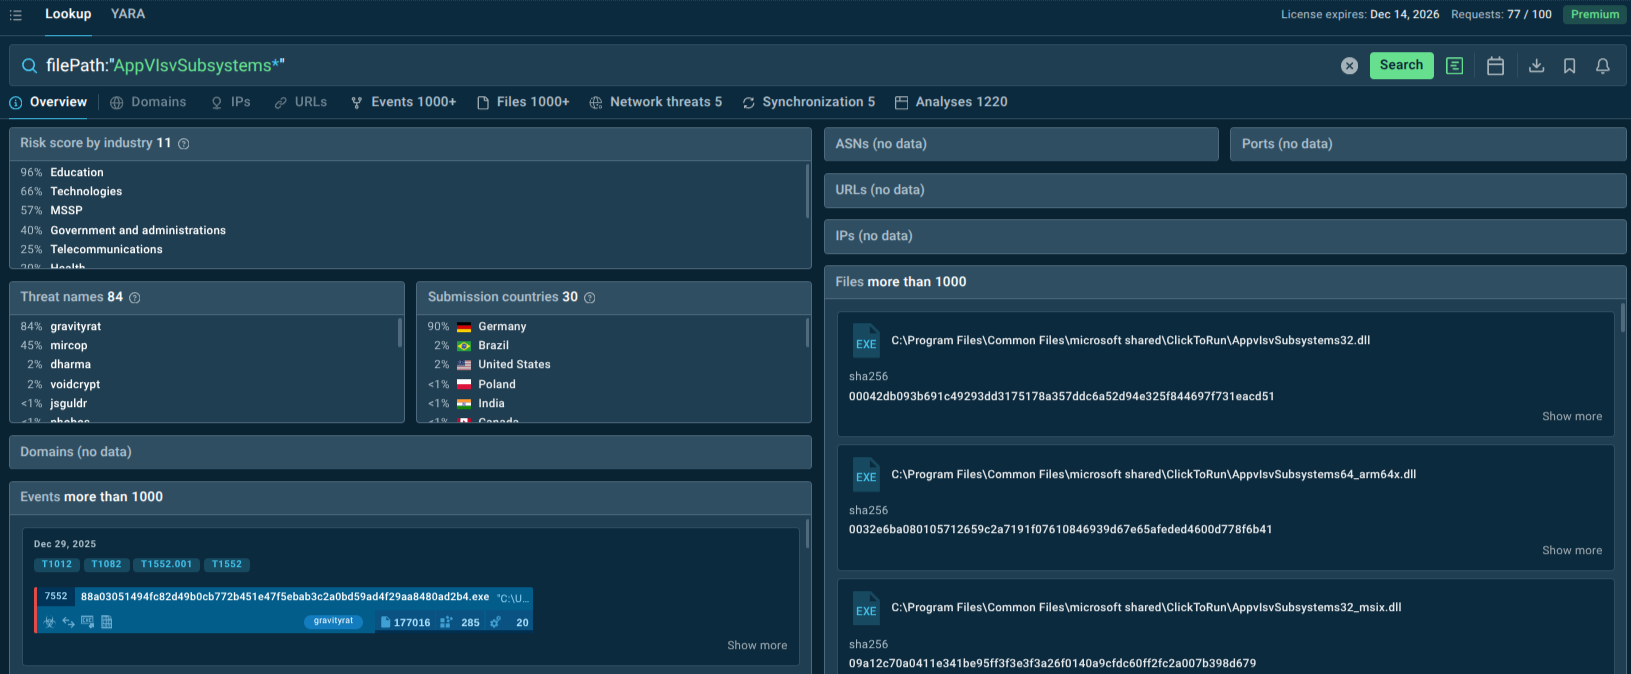
Utilize TI Lookup to query known indicators and discover related infrastructure and samples. Conduct proactive malware hunting using YARA rules specifically developed for GravityRAT detection.
A single IOC lookup can tell whether your business sector and geographical location are actively targeted by GravityRAT campaigns:
Conclusion
GravityRAT stands out among RAT families due to its persistence, stealth, and multi-platform reach. Its targeted distribution, virtualization evasion, and ability to exfiltrate sensitive data make it a formidable threat for enterprises and high-value individuals alike. Proactive defense, threat intelligence, and robust detection tooling are key to mitigating its impact.
Trial TI Lookup to start gathering actionable threat intelligence on emerging malware: just sign up to ANY.RUN.
Other malware & phishing threats
 CephalusCephalus is a targeted ransomware threat discovered in 2025. It’s known for infiltrating organizations that deal with sensitive data through compromised RDP access. It leverages DLL sideloading with a legitimate SentinelOne executable. Cephalus is able to exfiltrate data and destroy backup options. Its payload is also tailored to each victim, which makes identification and mitigation more complex.
 DarkTortillaDarkTortilla is a crypter used by attackers to spread harmful software. It can modify system files to stay hidden and active. DarkTortilla is a multi-stage crypter that relies on several components to operate. It is often distributed through phishing sites that look like real services.
 SmartLoaderSmartLoader is a Windows malware loader that uses multi-stage execution to deliver secondary payloads. It supports system discovery, screenshot capture, persistence through scheduled tasks, C2 communication, and anti-analysis techniques.
 ZloaderZloader is a banking trojan that uses webinjects and VNC clients to still banking credentials. This Trojan is based on leaked code from 2011, but despite its age, Zloader’s popularity has been only increasing through early 2020, when it relied on COVID-19 themed attacks.
 DarkVisionDarkVision RAT is a low-cost, modular Remote Access Trojan that gives attackers remote control of infected Windows hosts. Initially observed around 2020 and sold in underground marketplaces, DarkVision has become notable for its full feature set (keylogging, screen capture, file theft, remote command execution and plugin support) and for being distributed via multi-stage loaders in recent campaigns.
 SSLoadSSLoad is a malicious loader or downloader that is used to infiltrate target systems through phishing emails, perform reconnaissance and transmit it back to its operators delivering malicious payloads. To avoid detection, SSLoad employs various encryption methods and delivery techniques highlighting its versatile nature and complexity. It is believed to be a part of Malware-as-a-Service (MaaS) operation given its diverse delivery methods and implemented techniques.