PureCrypter
- 75
- Global rank
- 113
- Month rank
- 85
- Week rank
First identified in March 2021, PureCrypter is a .NET-based loader that employs obfuscation techniques, such as SmartAssembly, to evade detection. It has been used to distribute malware families including AgentTesla, RedLine Stealer, and SnakeKeylogger. The malware is typically delivered through phishing campaigns and malicious downloads, often masquerading as legitimate files with extensions like .mp4 or .pdf. PureCrypter utilizes encryption and compression to conceal its payloads and can inject malicious code into legitimate processes to maintain persistence on the infected system.
- Loader
- Type
- Unknown
- Origin
- 2 March, 2021
- First seen
- 19 October, 2026
- Last seen
How to analyze PureCrypter with ANY.RUN
IOCs
IP addresses
- 142.251.14.113
- 150.171.109.106
- 48.192.1.65
- 142.251.154.119
- 150.171.109.105
- 150.171.27.11
- 2.16.202.65
- 23.52.181.212
- 23.32.238.193
- 92.122.215.97
- 92.123.104.66
- 142.251.14.139
- 142.250.154.95
- 48.209.138.168
- 2.20.142.123
- 142.251.13.138
- 192.178.183.94
- 150.171.27.10
- 74.178.240.61
- 23.207.210.139
Hashes
- 5c3a5b578ab9fe853ead7040bc161929ea4f6902073ba2b8bb84487622b98923
- cc5dacf370f324b77b50dddf5d995fd3c7b7a587cb2f55ac9f24c929d0cd531a
- 388c5c95f0f54f32b499c03a37aabfa5e0a31030ec70d0956a239942544b0eea
- 8ff00d859349a3ea206706cdd3fa2762ae7c8efe2fdd33a95a72fee45aac6bc4
- f9d31b278e215eb0d0e9cd709edfa037e828f36214ab7906f612160fead4b2b4
- ec1702806f4cc7c42a82fc2b38e89835fde7c64bb32060e0823c9077ca92efb7
- ecc8d7540d26e3c2c43589c761e94638fc5096af874d7df216e833b9599c673a
- 20fb68d08674a2fa9fcb64a6cc6b299ef0112429ea96bee5d48d883c0a7aec2f
- 8c471cab38a1696289186d01b06ff6af2a888852dc18d6fb8d2a0e54898104ed
- f8e7cd835195e4eff7855d20676484ca75f7e7e4fe5b13164fc926b365e1dea0
- 0f40159d314caf1297ae650558f16eec539e44870396fa0b18164ba8762b0225
- 46b5ecada4edb2585f87953f7847aefc938be2404b9d9455c772b97295b7b1cb
- 951ea521116baf347ce89b628eabc22479fb8e3edfb7597659db2174fbb59804
- e87b3d155c7582d4c1d889308b58f84e8fe90a1581014b21b785d6694bd156cc
- e0cb362a73d69bad940a018881701b5f2a8527c13c3f5acbbea43b8820dfc199
- 84acd485899333cbdf5ad1f68d8c31658d5ecc9ee8dddf62098a2218687d7e77
- 15af1d2e507ede3610b17309b6cfd203563c1964aed4df9787f6fbea7ee50fd8
- c6d35100b5f200f20afb36bdc635516bc564cedfad90ab027f666fe2be2fdb84
- 421174da1c85229e304d97aa2b12ca7b0e4f47e9be54993b82bd56fa4e7a4ea2
- 8bebbbf8b72c0f834c6445ed3d84011f5adf29c43915d23f357907a93a4829ad
Domains
- redirector.gvt1.com
- oneocsp.microsoft.com
- accounts.google.com
- crl.microsoft.com
- assets.msn.com
- edge.microsoft.com
- client.wns.windows.com
- c.msn.com
- self.events.data.microsoft.com
- go.microsoft.com
- ogads-pa.clients6.google.com
- clients2.googleusercontent.com
- sb.scorecardresearch.com
- clientservices.googleapis.com
- ecs.office.com
- clients2.google.com
- login.live.com
- google.com
- www.gstatic.com
- ntp.msn.com
URLs
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
- https://www.bing.com/dsb/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=us&setlang=en-us&clientdatetime=10%2f19%2f2026%2c%201%3a52%3a54%20am
- https://login.live.com/rst2.srf
- https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
- https://www.bing.com/th?id=odswg.07bae8d4-9f7f-4621-a752-18358a102dfc&pid=dsb
- https://login.live.com/ppsecure/deviceaddcredential.srf
- https://th.bing.com/th?id=odswg.iotdlocalicon&w=16&h=16&c=1&rs=1&p=0
- http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
- https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
- https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
- https://slscr.update.microsoft.com/sls/ping
- https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
- https://64.89.161.158/ping
- https://64.89.161.158/plugin
- https://64.89.161.158/userinfo
- http://clients2.google.com/time/1/current?cup2key=8:r0dq3hizluok6qrofxxcislglv3mmbwqloq8reriquu&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Last seen at
- exe
- exe
- exe
- chatgpt.exe
- bazaar.abuse.ch
- 04510f9d11f433e48517273b05f3f800d73c16bca0b2b4a9afdaf3612550239e.exe
- f67f2fa47b7335ecfbfc059f1639f688321457a7a847c8d9f5156f35ac5ce814
- f9dca219a2403dbe79315dd5698d5eb293e5473f11be2ca438f5084c75ae7ac8
- edfcce66ccde72dc5a38d4ef5d0ca3206ec3c319586173f4b2d209d724ae6183
- 4e417fd6cce7dbff53412a820f4813d01da0e7f20e7615220aaa1372cc59db83
What is PureCrypter malware?
PureCrypter is a .NET-based loader malware first observed in March 2021. It is designed to deploy various payloads, including remote access trojans (RATs), information stealers, and other malicious tools on compromised systems. The malware is often sold on underground forums, with prices ranging from $20 to $60 per build, making it accessible to a wide range of cybercriminals.
The malware was developed by a threat actor known as PureCoder, who markets it as a customizable and reliable loader for spreading malware. PureCrypter has been linked to notable campaigns distributing AgentTesla, SnakeKeylogger, RedLine Stealer, and AsyncRAT, targeting individuals and organizations worldwide.
PureCrypter has been used in campaigns targeting financial institutions, healthcare organizations, and individual users. Its ability to deliver a wide variety of malware makes it a versatile and dangerous tool in the hands of cybercriminals.
To see how PureCrypter actually operates, you can upload its sample into ANY.RUN sandbox and check its behavior inside a secure environment.
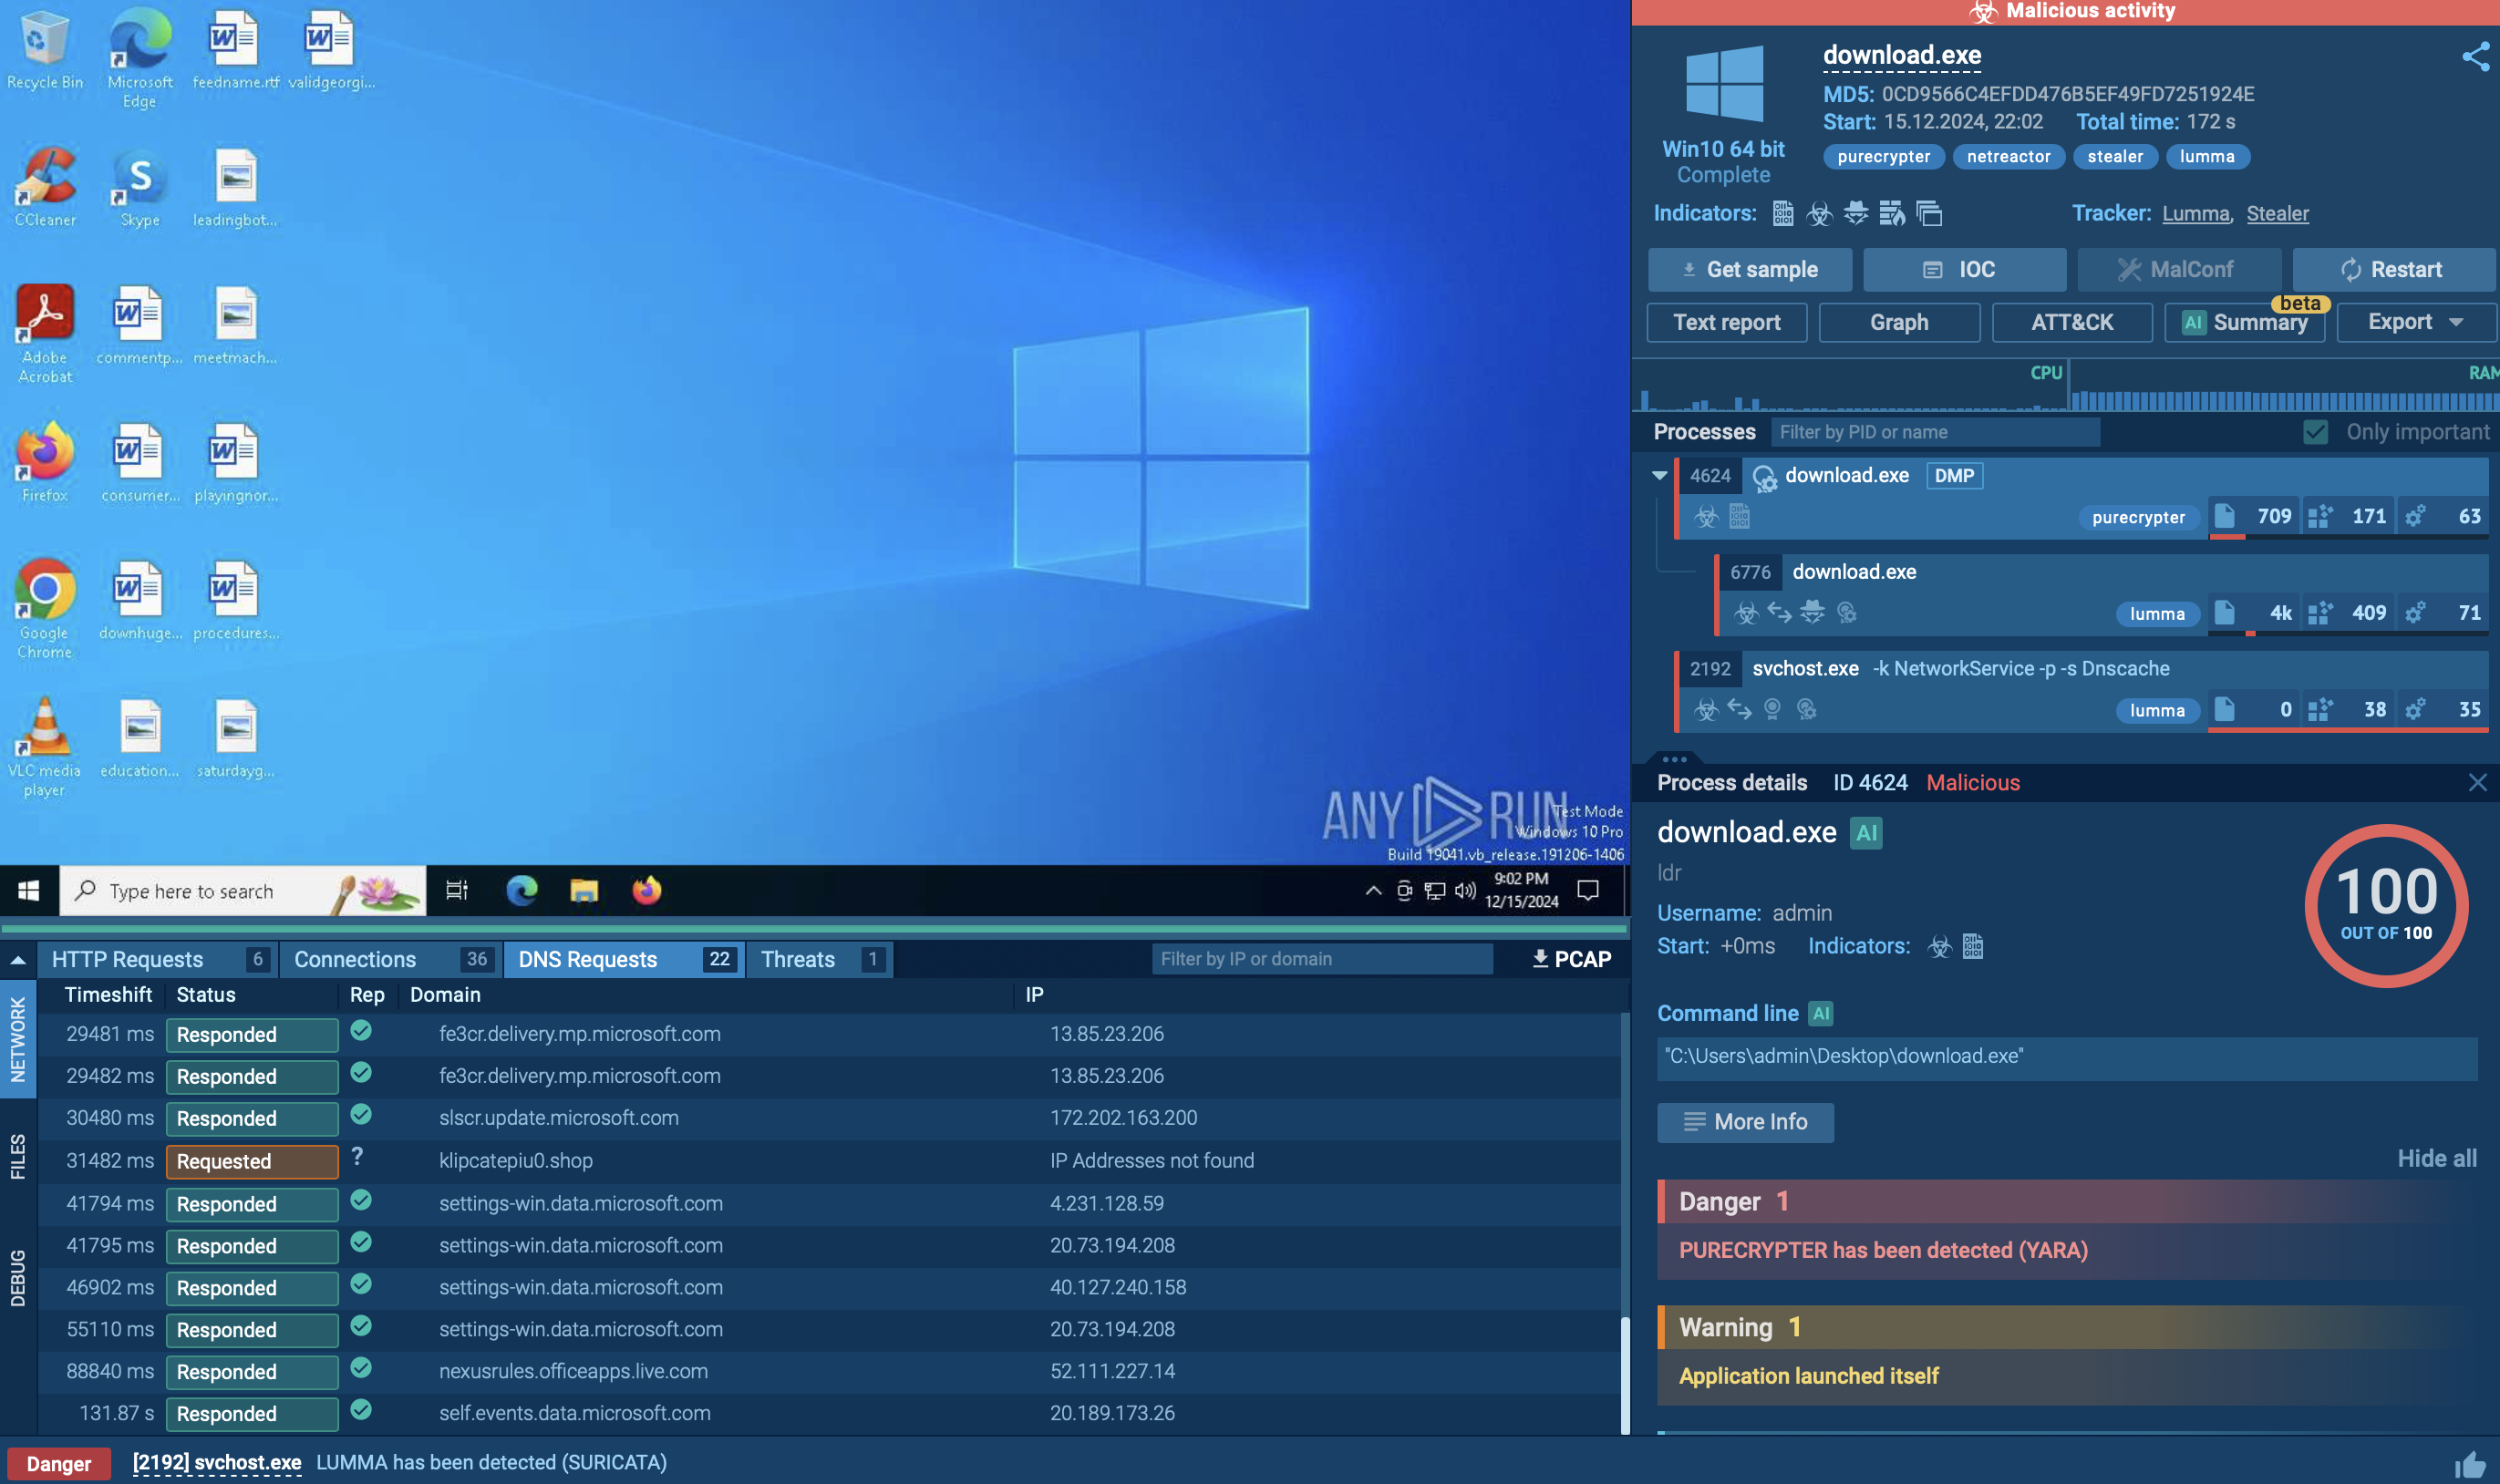
PureCrypter malware technical details
The primary functionalities and features of PureCrypter include:
- Deploys various malware types such as AgentTesla, SnakeKeylogger, RedLine Stealer, and AsyncRAT.
- Uses SmartAssembly to obfuscate its code, making it difficult for antivirus tools to detect.
- Encrypts and compresses payloads to conceal malicious activities during delivery.
- Injects payloads into legitimate processes to bypass security measures and evade detection.
- Ensures continued presence on the infected system through registry modifications and startup entries.
- Sold on underground forums with options for customization, making it accessible to cybercriminals with varying technical expertise.
- Delivered via phishing campaigns with malicious attachments (e.g., disguised .mp4, .pdf, or executable files).
Often used in campaigns against financial, healthcare, and individual targets globally.
PureCrypter malware execution process
To see how PureCrypter operates, let’s upload its sample to the ANY.RUN sandbox.
PureCrypter typically spreads through malicious downloads or phishing attacks. Once a user executes the infected file, the malware begins its execution chain. Upon execution, PureCrypter decrypts its payload in memory to avoid leaving traces on the disk, making it harder for traditional antivirus solutions to detect. The decrypted payload is then injected into a legitimate system process, helping the malware blend in with normal system activities and further evade detection.
In our case, the targeted process is MSBuild, but PureCrypter may also inject into other legitimate system processes, such as InstallUtil.
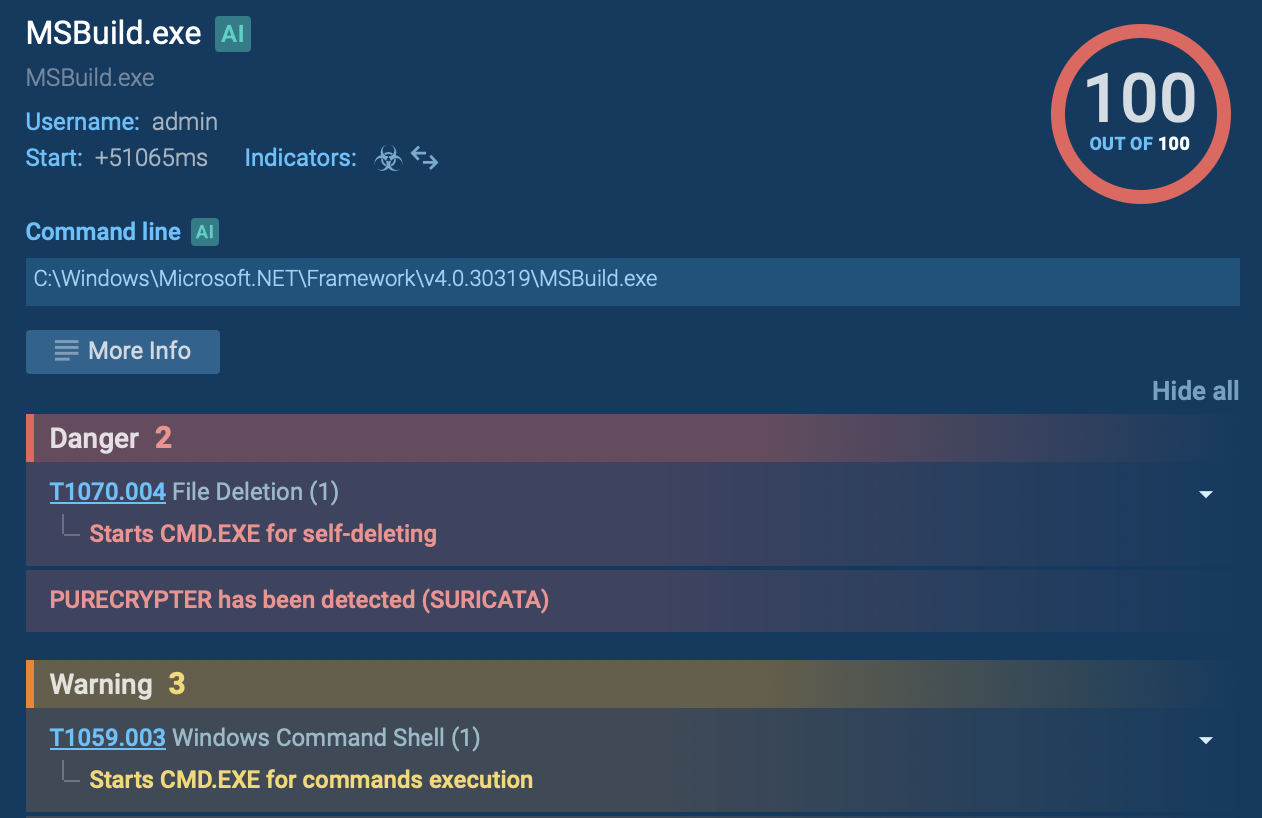
In addition to process injection, PureCrypter leverages various trusted system tools. For example, in this scenario, it ran PowerShell to add Product.exe and its associated processes to the antivirus exclusion list, reducing the likelihood of detection.
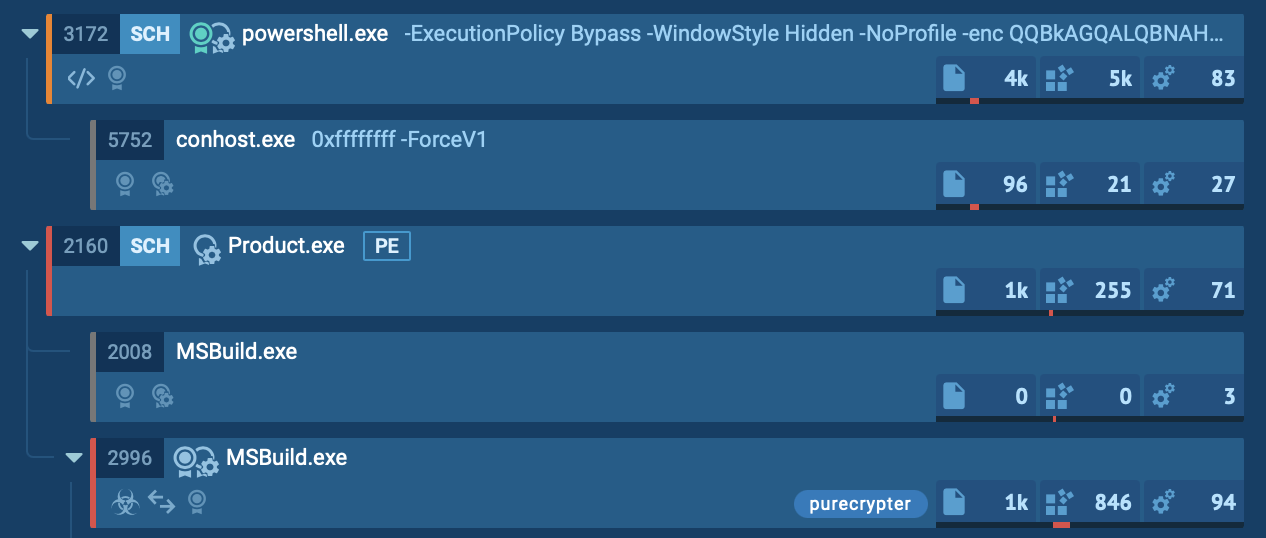
After establishing itself within a legitimate process, PureCrypter connects to its command-and-control (C2) server. Through this connection, attackers can issue commands, download additional payloads, or exfiltrate data from the infected machine. Ultimately, PureCrypter executes its primary malicious payload, which can range from ransomware or spyware to other forms of malware designed to steal data or compromise the system.
To ensure persistence after a reboot, PureCrypter may modify registry entries, create scheduled tasks, or use other persistence techniques. It can also self-delete after execution to erase evidence of its presence.
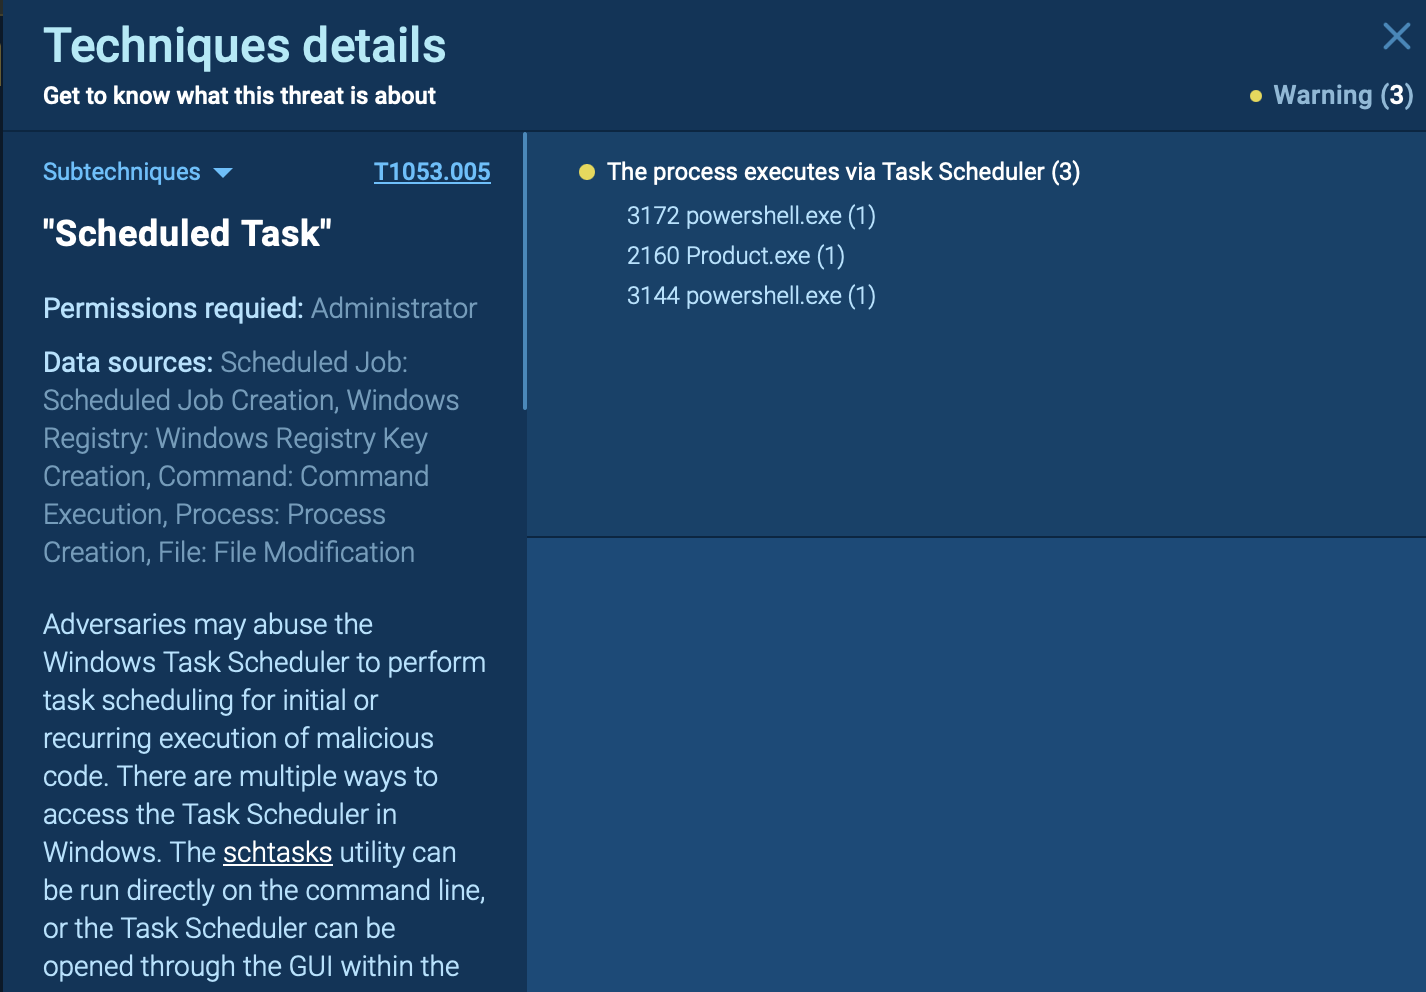
In our example, the injected MSBuild process ran the Command Prompt (CMD) to terminate itself and remove the initial Product.exe file.
Gathering Threat Intelligence on PureCrypter Malware
To collect up-to-date intelligence on PureCrypter, use Threat Intelligence Lookup.
This service provides access to a vast database with insights from millions of malware analysis sessions conducted in the ANY.RUN sandbox. With over 40 customizable search parameters, users can gather detailed data on threats, including IPs, domains, file names, and process artifacts.
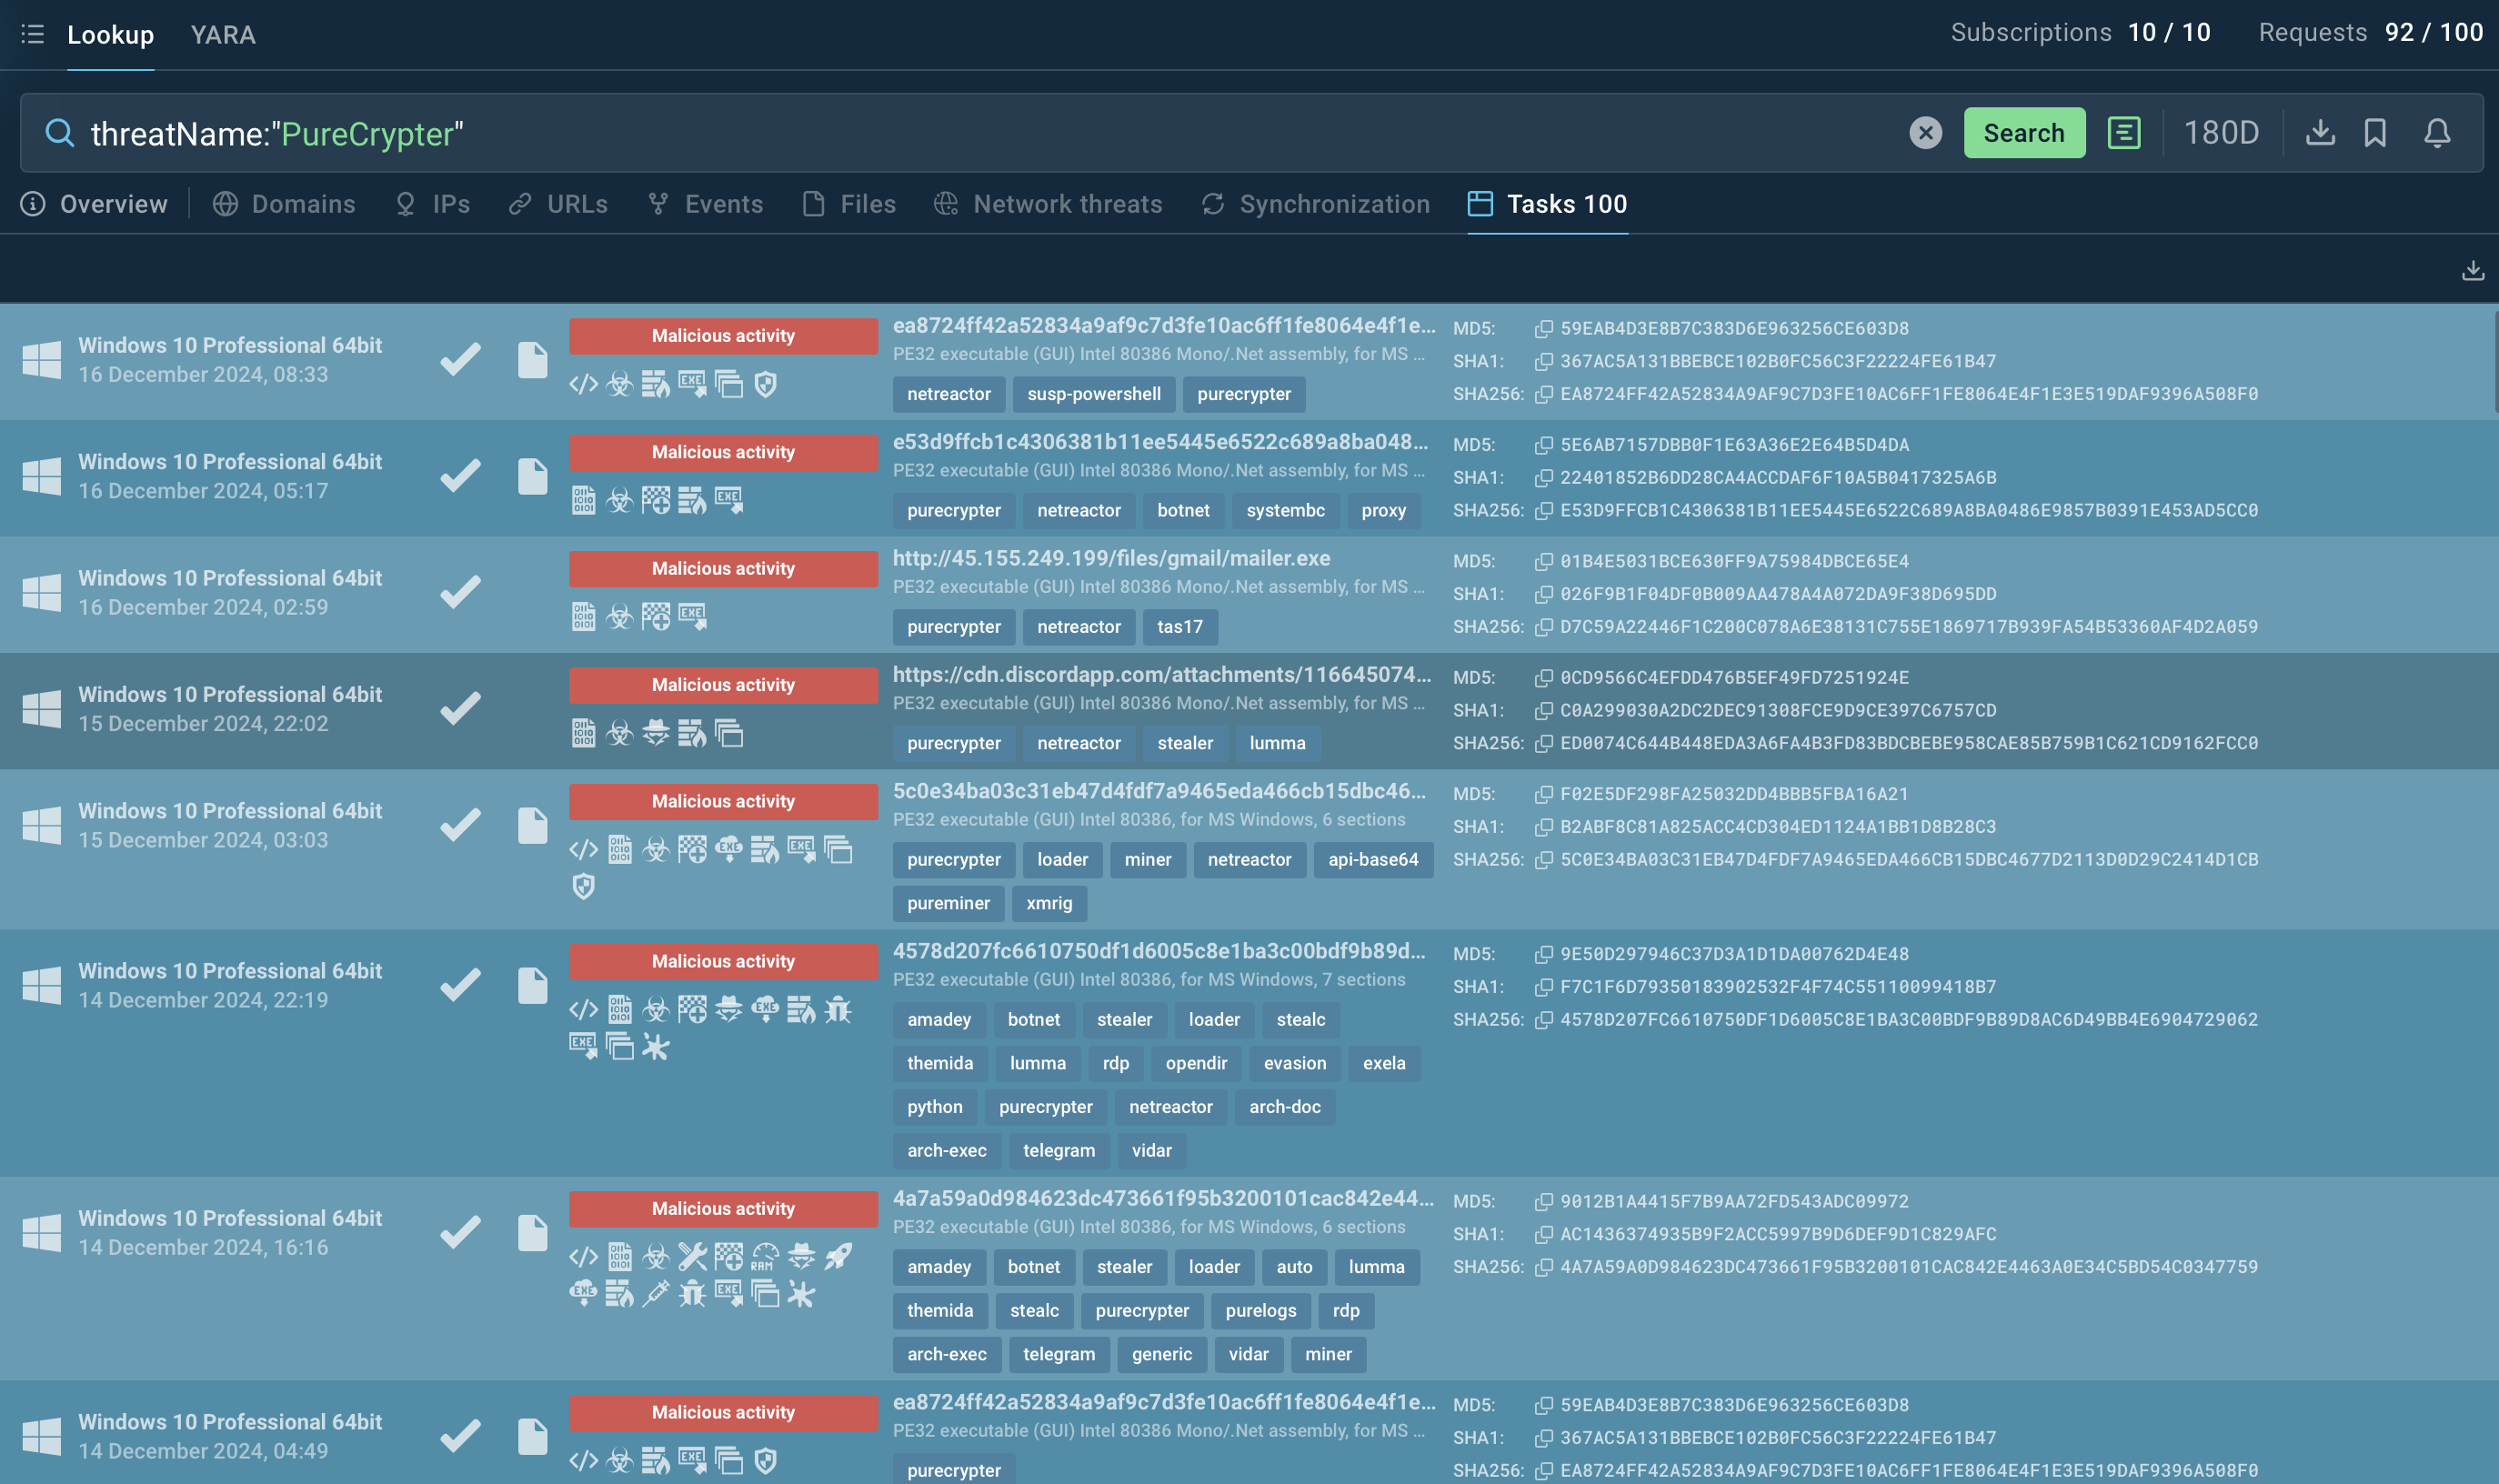
For instance, to investigate PureCrypter, you can search by its threat name or use a related artifact. A query like threatName:"PureCrypter" will retrieve all associated samples and sandbox results relevant to this loader malware.
Conclusion
PureCrypter is a dangerous malware capable of deploying various threats while evading detection through obfuscation and encryption. Tools like ANY.RUN can help to analyze suspicious files and URLs to prevent attacks.
ANY.RUN offers real-time malware analysis with features like visual execution chains and script tracing, helping users detect threats effectively.
Sign up for a free ANY.RUN account today and analyze unlimited malware attacks!
Other malware & phishing threats
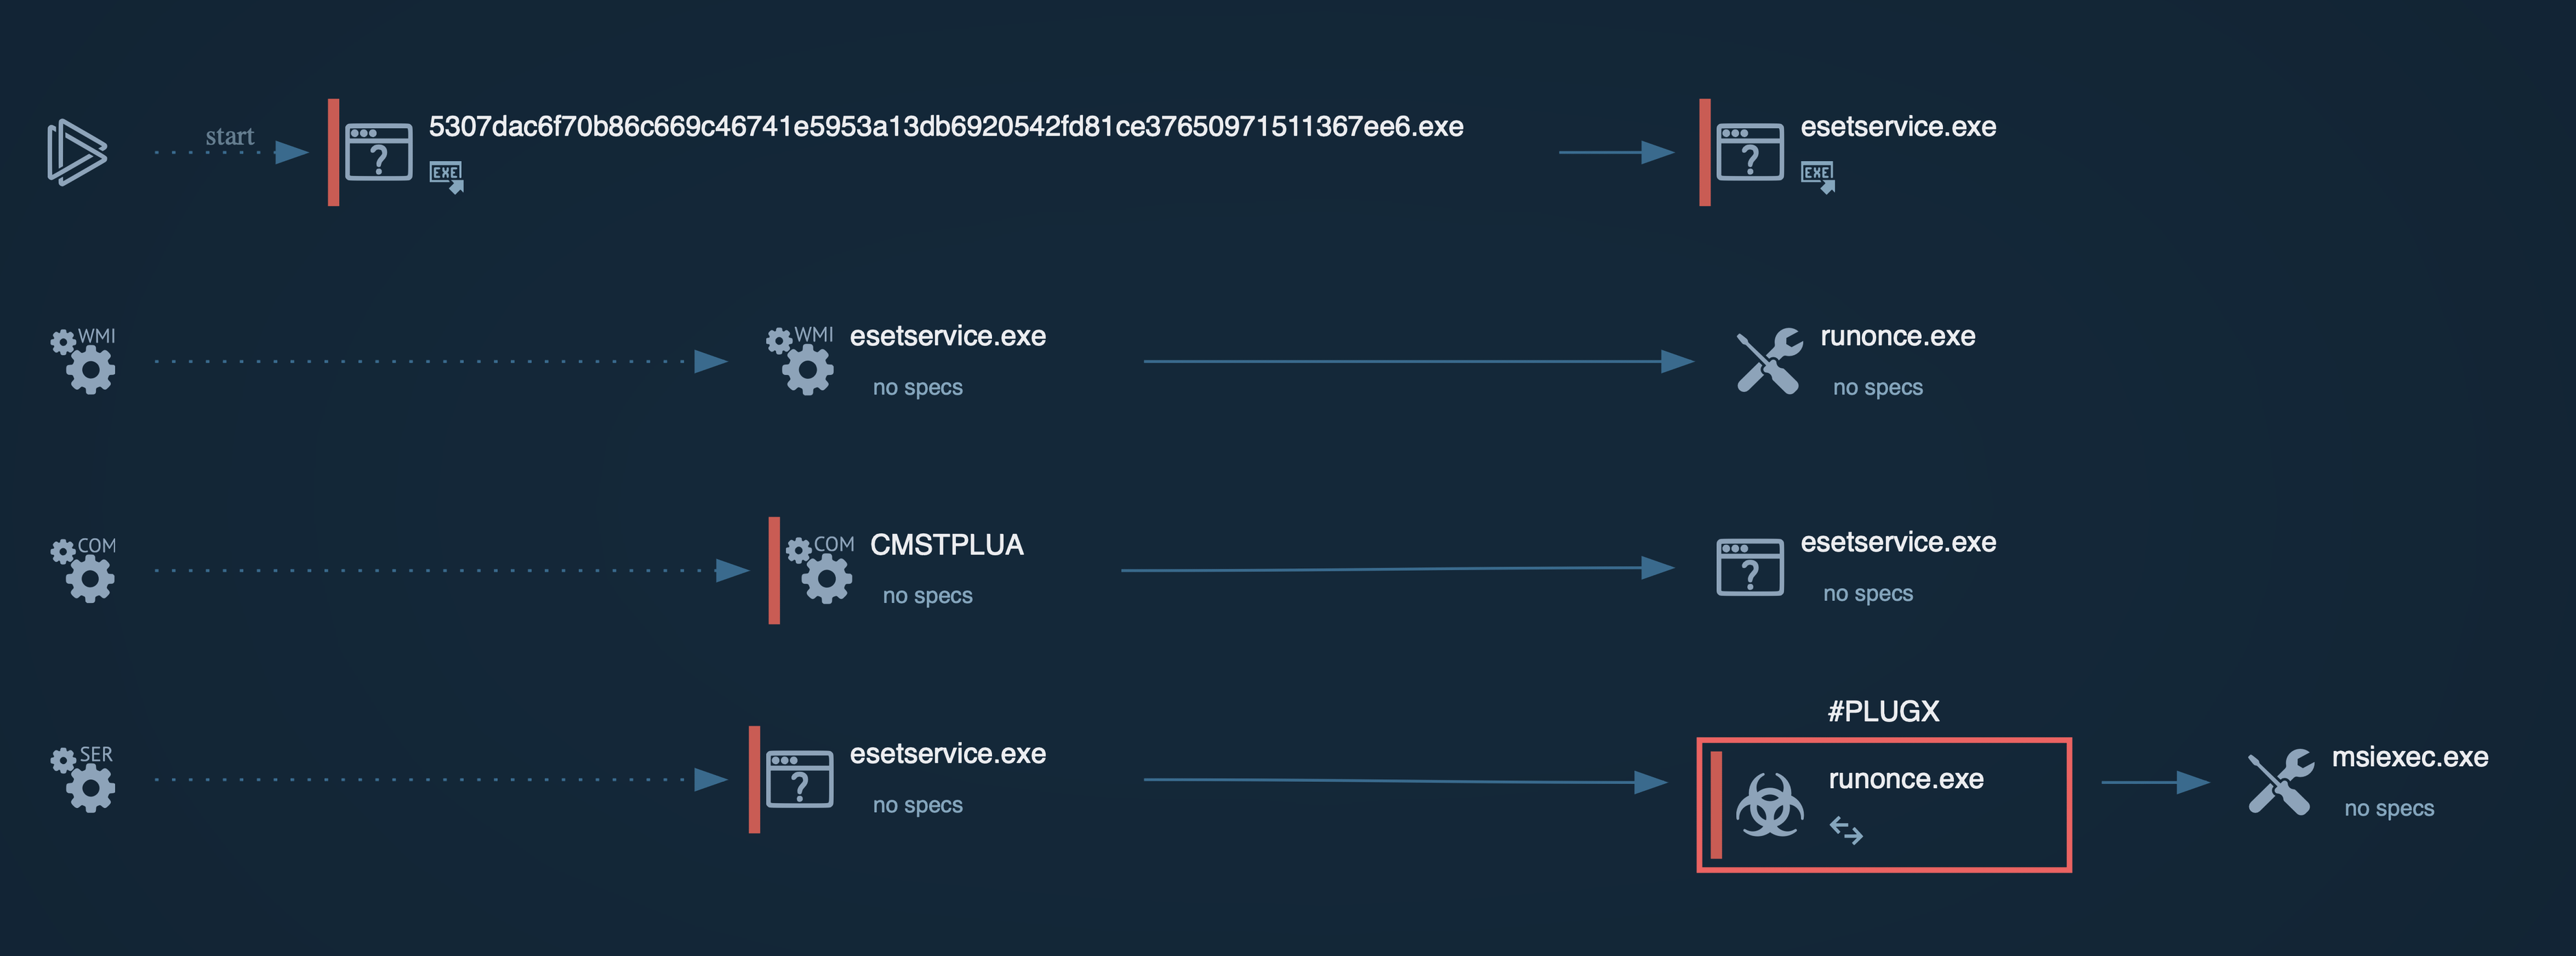 PlugXPlugX is a remote access trojan that is used extensively by Chinese APTs. The malware is primarily employed for spying on victims and can perform a variety of malicious activities, such as logging users’ keystrokes and exfiltrating information from browsers.
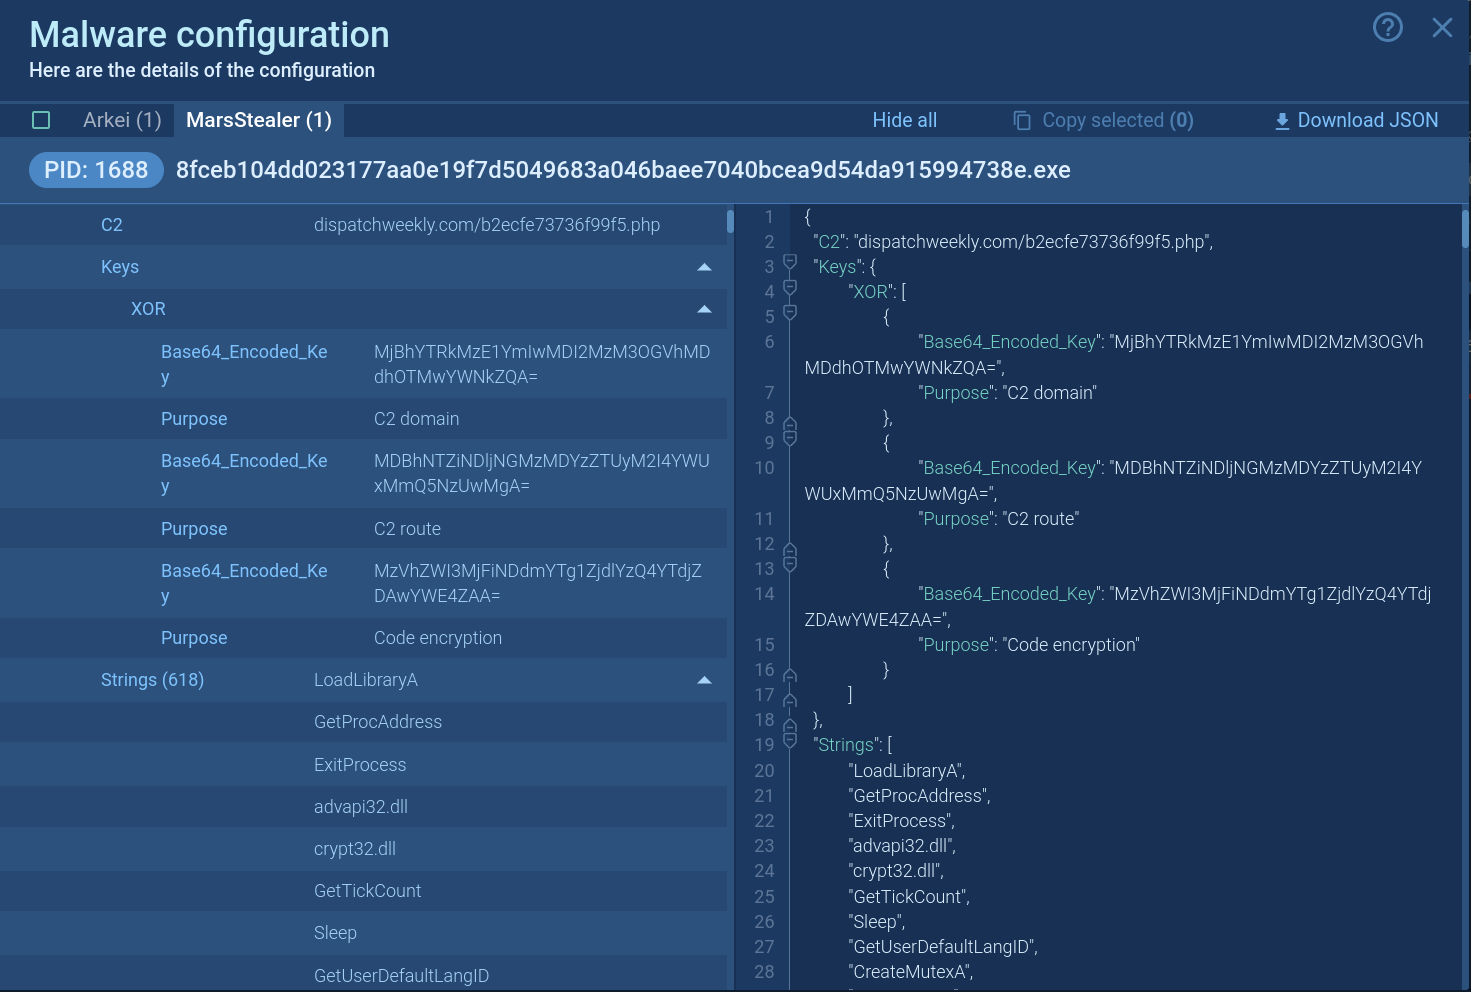 Mars StealerMars Stealer is a malware program designed to steal sensitive information from infected systems. It can access browser credentials, cryptocurrency wallets, and system information. The malware utilizes advanced evasion techniques and transmits stolen data securely through a C&C server.
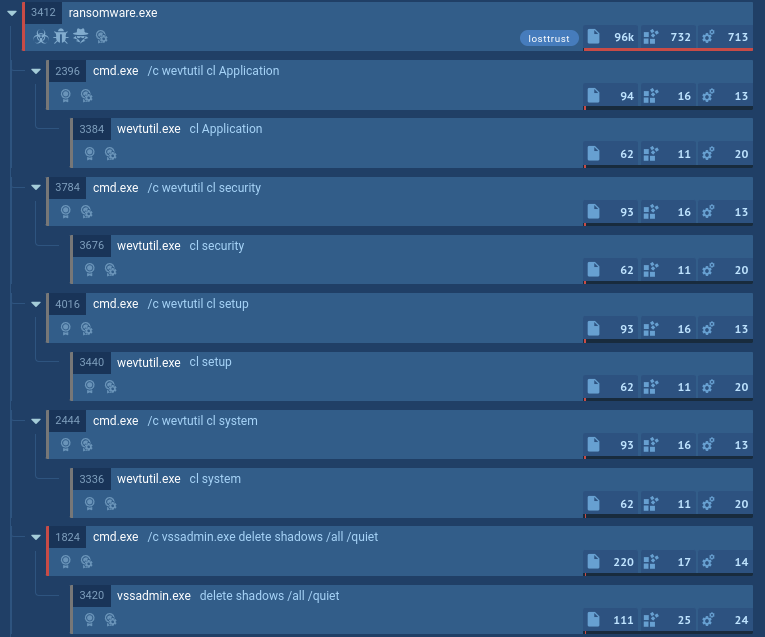 LostTrustLostTrust is a ransomware that has been active since March 2023. It is a multi-extortion malware, meaning that it not only encrypts data on the compromised system and demands a ransom, but also exfiltrates some of the critical files to the attacker. The criminals publish the stolen data on a special website, where dozens of companies are listed as victims of the malware.
 RiseProRisePro, an information-stealing malware, targets a wide range of sensitive data, including credit cards, passwords, and cryptocurrency wallets. By compromising infected devices, RisePro can steal valuable information and potentially cause significant financial and personal losses for victims.
 SnakeSnake is a modular keylogger written in .NET. Adversaries use this malware to exfiltrate confidential data, such as keystrokes, screen captures, and login credentials.